Category

Security

17posts

20 min

npm vs JSR vs npmx: How the Registry Model Shapes Your Supply Chain Risk

A developer security comparison of npm vs JSR vs npmx (which is a package browser, not a registry), the real alternative registries beyond both, what each registry model changes for supply chain attacks and attack surface, the attacks actually used in 2025 and 2026, and the layered defenses that hold up against them.

12 min

mTLS for Internal Services: Useful Security or Homelab Theatre, Hands-On

mTLS authenticates both sides of an internal connection, which closes a real hole on a LAN full of devices, and it does not fix application bugs, stop a compromised service, or survive root on the host. A hands-on look at the threat model, client certificates with Caddy and Nginx, service mesh identity, and the mobile apps that cannot present a certificate.

12 min

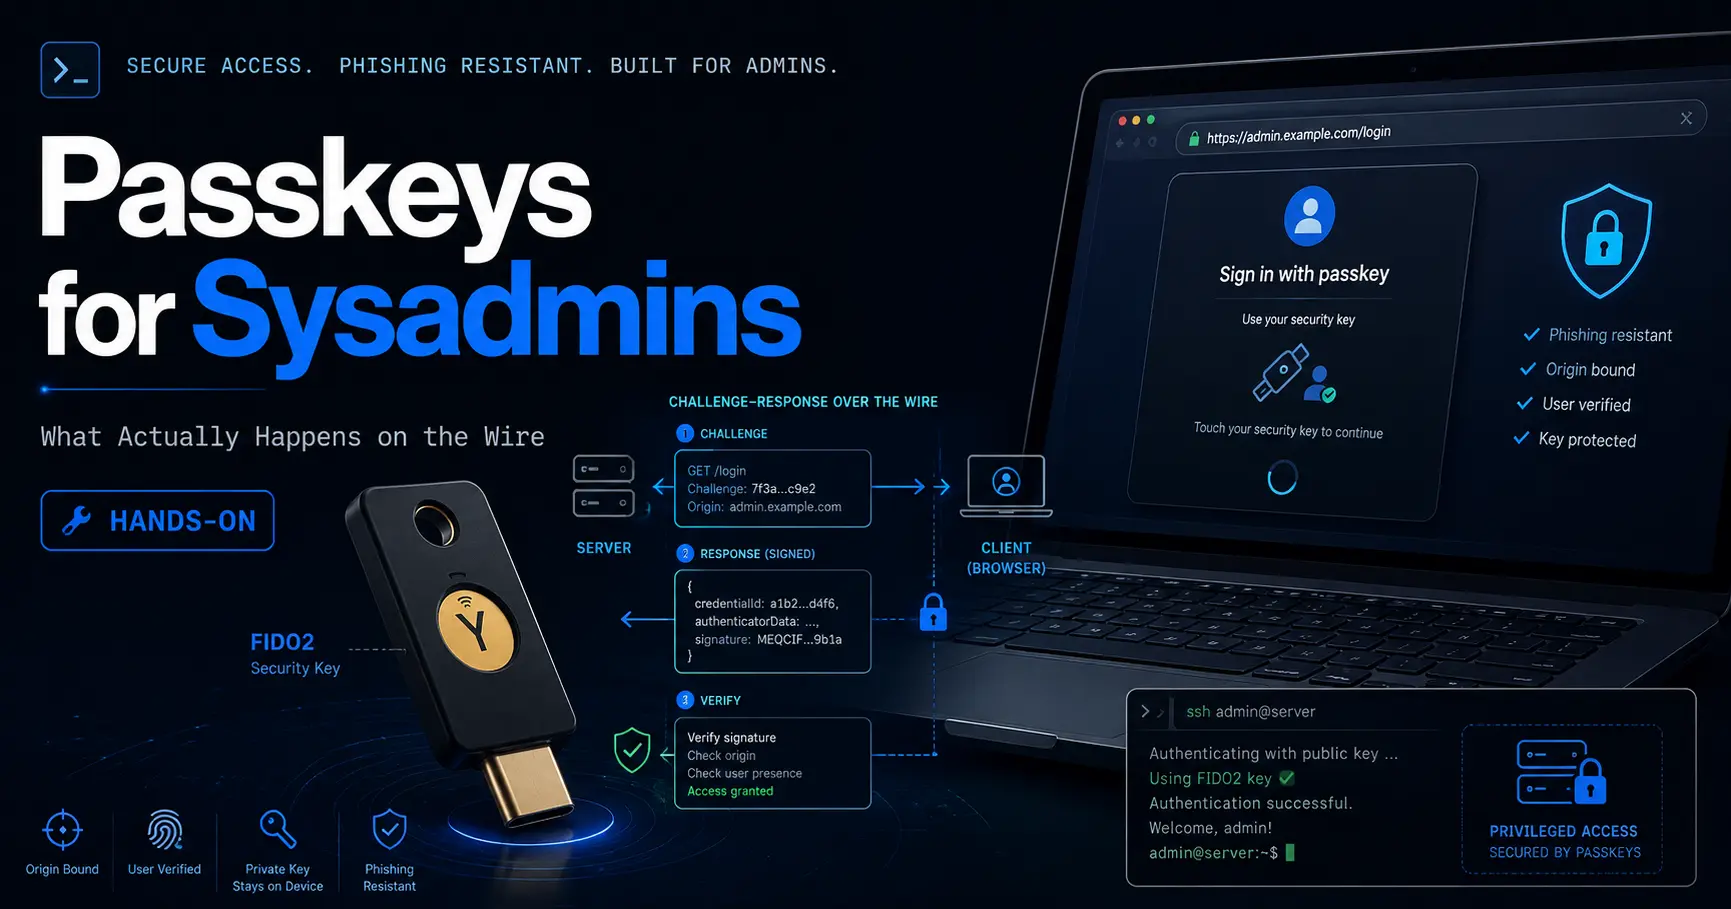
Passkeys for Sysadmins: What Actually Happens on the Wire, Hands-On

A sysadmin-grade walkthrough of what actually happens on the wire with passkeys and WebAuthn: the registration and authentication ceremonies, discoverable credentials, what sync really costs you, hardware keys, phishing resistance and its limits, recovery planning, FIDO2 SSH keys, and the honest list of where passkeys do not apply.

8 min

CrowdSec Behind Cloudflare: Who Actually Sees the Attacker's IP, Hands-On

When Cloudflare fronts your origin, CrowdSec only sees what your reverse proxy writes into the log: edge IPs unless trusted proxies are configured. A hands-on guide to CF-Connecting-IP, X-Forwarded-For spoofing, firewall-level versus app-level blocking, and the CrowdSec Cloudflare bouncer that moves the block to the edge.

10 min

SOPS + age: Secrets in Git Without Pretending Git Is a Vault, Hands-On

SOPS plus age is the git-native way to keep secrets out of plaintext commits: age key setup, .sops.yaml creation rules, the daily encrypt and decrypt workflow, GitOps integration with Flux and Argo CD, key rotation, a recovery strategy that survives a lost laptop, and the honest limits of the pattern.

11 min

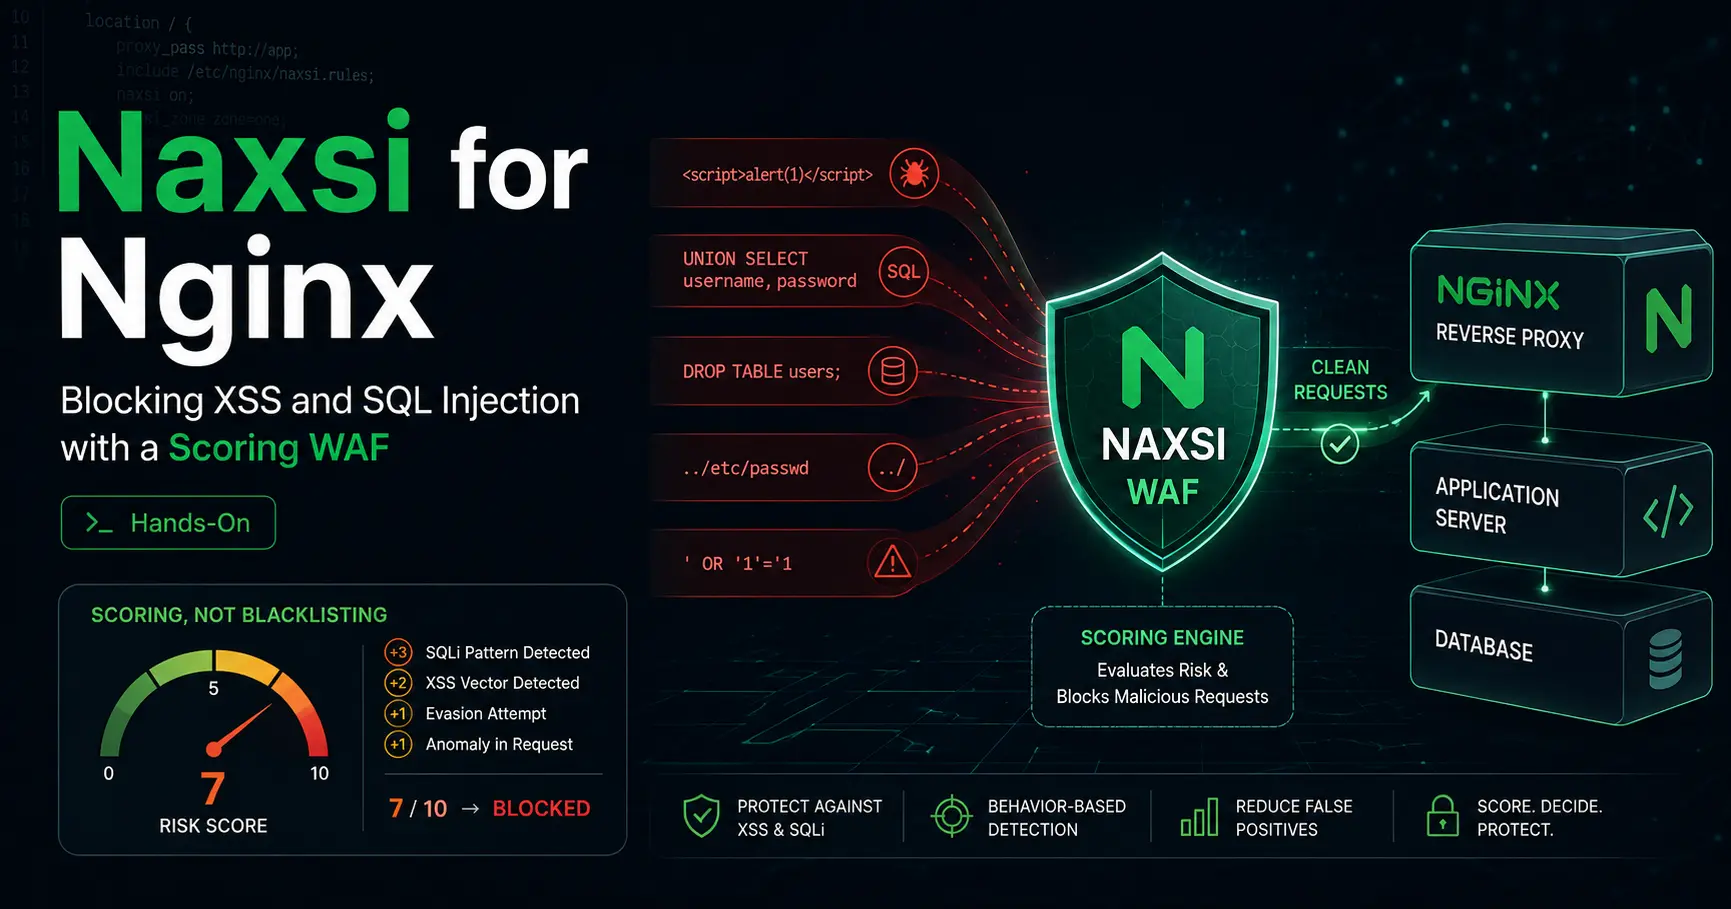
Naxsi for Nginx: Blocking XSS and SQL Injection with a Scoring WAF, Hands-On

A hands-on sysadmin guide to Naxsi, the Nginx Anti XSS and SQL Injection WAF module: how the scoring, deny-by-default model works, building and installing the maintained wargio fork on Debian, Ubuntu, and Fedora, learning mode and nxtool whitelists, what WordPress, Joomla, and Magento need to avoid false positives, the honest limits, and when ModSecurity is the better call.

16 min

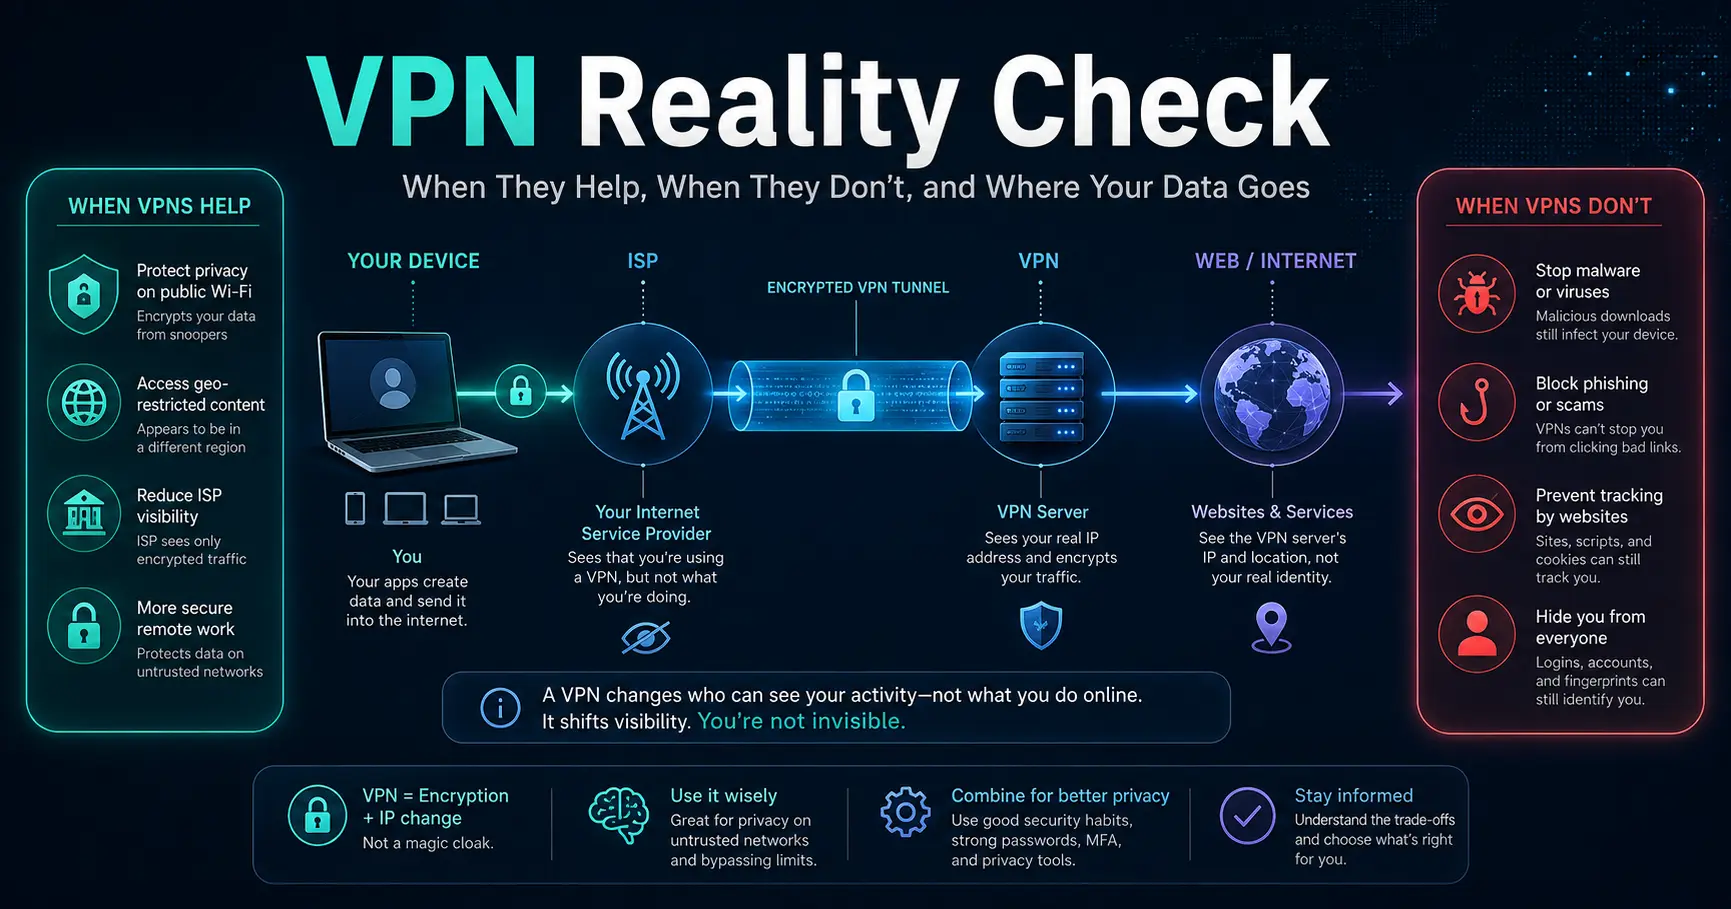
VPN Reality Check: When They Help, When They Don't, and Where Your Data Goes

A sysadmin's field guide to VPNs: what a VPN actually does to your traffic, the threat models it does and does not answer, how no-logs claims and audits really work, which providers pass the test, and a deep technical comparison of OpenVPN, WireGuard, and the proprietary protocols (NordLynx, Lightway, Catapult Hydra, Chameleon), plus a hands-on self-hosted WireGuard setup.

5 min

SMS-Based Two-Factor Authentication is No Longer Effective

SMS two-factor authentication was a real upgrade, but SIM swapping, SS7 interception, and real-time phishing have turned the code into a second password an attacker can read. Why it now gives a false sense of security, and what to use instead: TOTP apps, passkeys, hardware keys, and printed recovery codes.